 EN
 FR
 DE
 IT
 PT
 ES


SQL Server Security: Best Practices and Guide
SQL Server security has always been a pressing concern, even for the most experienced users. Regardless of your version, the SQL Server database is under constant threat because it contains valuable data that malicious actors seek to access.
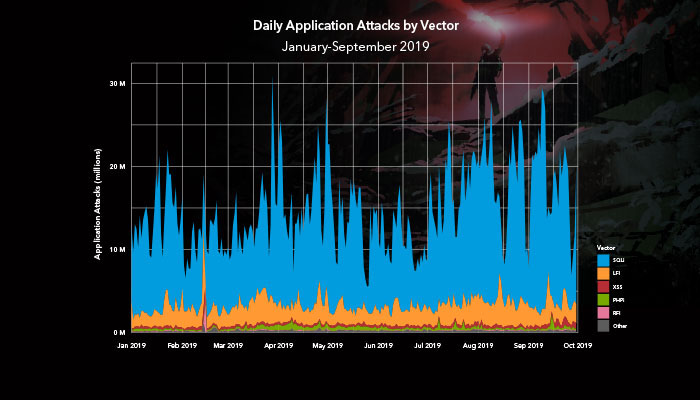
SQL injection attacks (SQLi) are straightforward to carry out yet potentially devastating, which makes them a favourite tool for hackers. The State of the Internet/Security Report showed that SQLi alone accounted for 77% of all application attacks in 2019. In an SQLi attack, hackers insert rogue SQL statements into an application's database query to manipulate or destroy data.
Securing SQL Server environments is one of the core responsibilities of database administrators. Fortunately, SQL Server is designed as a secure database platform, offering a range of features to encrypt data, restrict access and authorisation, and guard against theft, destruction, and other forms of malicious activity.
Despite these built-in defences, many organisations still fall victim to SQL database vulnerabilities, including injection attacks, credential-stuffing attempts, and other data-manipulation exploits.
The threat landscape is ever-present, but that does not mean you are powerless. To protect your organisation, database administrators and security professionals must understand the potential risks and take proactive steps to mitigate them.
Best practices for SQL Server security
SQL Server is one of the most widely used data platforms in the world, underpinning critical business operations and processes. It therefore provides a broad set of security tools to defend against malicious attacks and safeguard your instances.
However, relying on default security settings can leave gaps that attackers will exploit. The checklist below will help you harden your SQL Server environment effectively.
1. Conduct regular SQL Server security audits
Routine security, login, and server-authorisation audits are a fundamental safeguard against potential attacks and support forensic analysis after a data breach. An enterprise-wide SQL Server security audit is not only good practice — it has become a legal requirement under regulations such as HIPAA and GDPR.
Start by defining what you want to audit. Your server audits should cover the following areas:
• User logins
• C2 audit tracing
• Common compliance criteria
• Login verification
• Server configuration
• Policy changes
• SQL Server audit specifications
• SQL Trace
• Extended Events
• Change Data Capture
• DML, DDL, and logon triggers
A routine audit can improve the health of your database and network. For example, if a query fails to execute, an audit can pinpoint the cause — whether that is a security threat or simply an error in the SQL operation sequence.
Likewise, repeated failed logins, deletions of restricted objects, and unexpected changes to settings or permissions may all signal an intrusion attempt. Regular audits help you spot these warning signs and respond before further damage occurs.
2. Enforce a strict password policy
Every database administrator account should have a strong password to guard against brute-force attacks.
• Use at least 10 characters, mixing numbers, upper- and lower-case letters, and special characters. Alternatively, use a passphrase of at least 15 characters including letters and numbers.
• Avoid easily guessed passwords such as “password”, “qwerty”, or names and dates of birth. Never reuse the same password across systems.
• Rotate passwords regularly.
• Use a password manager with a strong master key to store credentials securely.
3. Keep the system lean
Unnecessary software and additional applications give hackers more attack surface on your SQL database server. Multiple applications are also harder to manage and quickly become outdated.
Outdated or unpatched applications introduce vulnerabilities that attackers can exploit to execute unauthorised code via SQL injection or other vectors.
Limit the installed SQL database components and features to those required for specific tasks. This reduces resource consumption, simplifies administration, and minimises security risk.
4. Apply the principle of least privilege
The principle of least privilege is a cornerstone of information security. It states that every account should be granted only the minimum permissions needed to perform its intended function.
Based on this principle, decide which accounts should run which database services. Ideally, assign a separate account to each service so that if one is compromised, the others continue to operate normally.
Common account types for SQL Server services include:
• Domain user account — The most widely used type for running SQL Server services; relatively secure because it has no administrator rights.
• Active Directory Managed Service Account — More secure than a domain user account; you cannot log on to the server with it and it handles password rotation automatically.
• Local user account — Suitable for non-domain environments.
• Local system account — Has full privileges and unrestricted access to all local resources. Because it grants far more access than SQL Server needs, avoid using it for services.
• Network service account — Fewer privileges than a system account but more network access than a standard user. Avoid if possible.
• Virtual service account — Similar to an AD-managed service account but usable without a domain. It is a built-in network service account with its own unique identity, making it an excellent choice for SQL services.
5. Maintain a robust backup strategy
Always back up your SQL database and store copies in multiple locations outside your primary network. Use reputable third-party SQL recovery tools to address issues such as corruption or inaccessibility of database files.
Remember to encrypt your backups as well. A backup contains the same sensitive data as the live database and should be protected accordingly. Apply the same access restrictions, security measures, and monitoring controls to your backup data.
6. Use a suitable SQL Server monitoring tool
A robust monitoring tool should scan database application processes and track configuration changes on the server. It should quickly flag errors, sessions, and individual SQL statements that could expose sensitive information.
Bear in mind that the monitoring tool itself can become a security risk if it is not properly secured. Ensure the tool follows modern security practices so it supports — rather than undermines — the long-term health of your database and network.
A well-chosen monitoring tool will help you defend against common attacks, troubleshoot performance issues, and keep your systems running smoothly.
Summary
SQL Server provides a wealth of features to support and secure database applications, but no platform can predict every future threat. That is why it pays to follow established best practices and stay alert to evolving risks.
By combining regular audits, strict access controls, a lean installation, and reliable backups, you can build a solid security strategy that keeps your SQL Server databases well protected.
If you have any questions, feel free to contact us or use our live chat.




